You signed in with another tab or window. Reload to refresh your session.You signed out in another tab or window. Reload to refresh your session.You switched accounts on another tab or window. Reload to refresh your session.Dismiss alert
{{ message }}
Repository navigation
fix(auth): default to classic token guidance and warn about fine-grained limits (#594) - #604
When users use GitHub Fine-grained Personal Access Tokens (PATs) to manage stars:
GitHub restricts Fine-grained PATs to the designated Resource Owner. Calling DELETE /user/starred/{owner}/{repo} or PUT /user/starred/{owner}/{repo} on repositories belonging to other users or organizations often results in 403 Forbidden (Resource not accessible by personal access token) or 404 Not Found if scoped via "Only select repositories" or blocked by organization PAT policies.
Fine-grained PATs do not support GitHub Lists (starred lists) API due to lack of user scope support.
Previously, the token permissions dialog defaulted to the "Fine-grained" tab without explaining these restrictions, causing users to mistakenly assume Fine-grained PATs are recommended and fully supported for all star management operations.
Changes
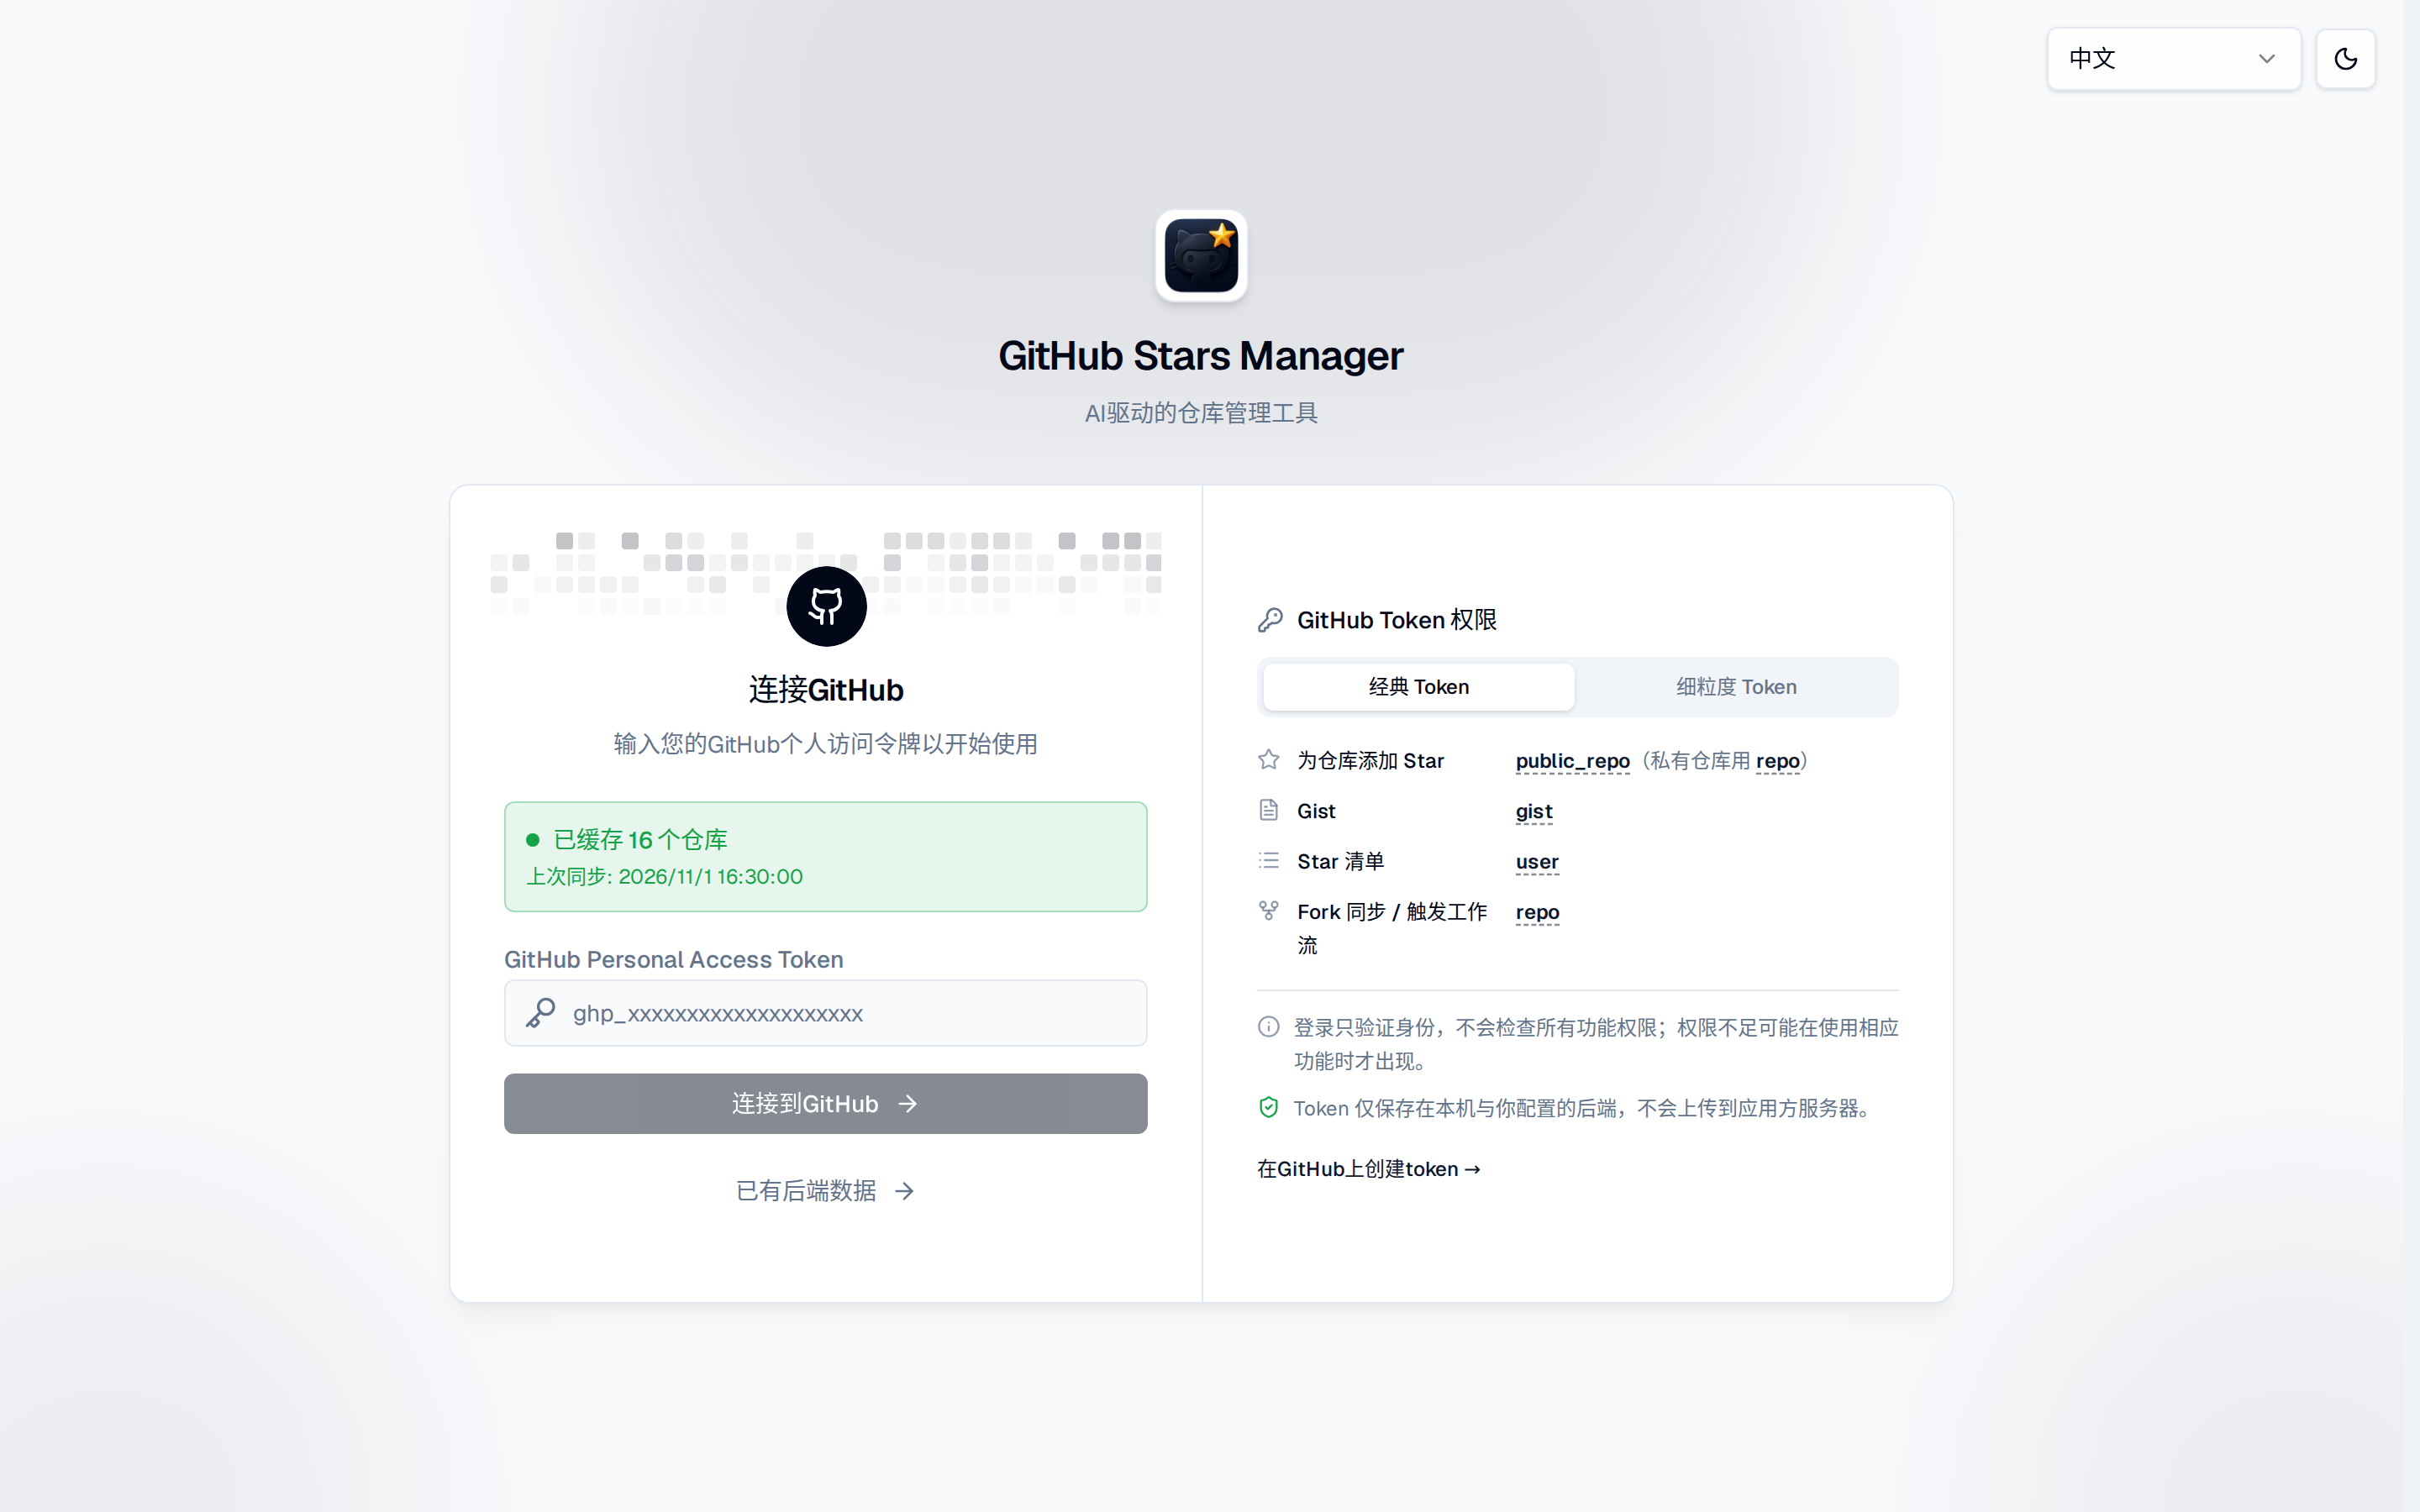
Default to Classic Token: In GitHubTokenPermissions.tsx, set the default active mode to 'classic' and ordered the "Classic Token" tab first.
Pre-fill Scopes for Classic Token Creation: Updated the GitHub token creation link for classic mode to prefill the required scopes (public_repo,gist,user): https://github.com/settings/tokens/new?description=GithubStarsManager&scopes=public_repo,gist,user
This lets users generate a correctly scoped token with a single click.
Fine-grained Limitations Callout: When users switch to the "Fine-grained Token" tab, displayed a clear warning callout highlighting:
Inability to reliably star/unstar repositories across organizations or third parties (403 errors).
Inability to sync Star Lists (GitHub API limitation).
Recommendation to switch to Classic Token with a one-click button.
Localization & Parity: Added translations across all 10 supported languages (zh, zh-TW, en, ja, ko, de, es, fr, pt-BR, ru).
Tests: Updated src/components/LoginScreen.test.tsx to verify default tab selection, limitation callouts, tab switching, and dynamic creation URLs.
Verification
npm run check:i18n (passed)
npm run typecheck (passed)
npm run lint (passed)
npm test -- --run (all 195 test files, 2416 tests passed)
Summary by CodeRabbit
新功能
登录时默认选择经典 GitHub Token,并根据所选类型提供对应的创建链接。
细粒度 Token 面板现会说明其在管理组织或他人仓库星标、同步 Star 列表方面的限制,并提供切换到经典 Token 的入口。
This changes the token guidance in the login dialog to recommend classic tokens by default and warns about fine-grained limits. No concrete merge-blocking issue was found, so the risk is minimal.
Pre-merge checks: 4
Check name
Status
Explanation
Description Check
Check skipped - CodeRabbit’s high-level summary is enabled.
关联 Issue:[#594]。该 Issue 是用户提问,描述“Token 已添加权限,取消 Star 仍提示无权限”。Issue 未提供明确验收标准。PR 的目标是处理该问题的可能原因:Fine-grained PAT 对他人或组织仓库的 Star 操作受限,且不支持 Star Lists。实现内容如下。(1) `src/components/GitHubTokenPermissions.ts…
File: No configuration file from this repository applied
Commit: Unavailable
Layers: Organization UI
Review profile: CHILL
Plan: Advanced
Run ID: d37c17bd-d6a0-4dc4-b9fb-290087227a4d
Commits
Reviewing files that changed from the base of the PR and between 32f877f and f3c82f1.
Files selected for processing: 12
src/components/GitHubTokenPermissions.tsx
src/components/LoginScreen.test.tsx
src/locales/de/login.json
src/locales/en/login.json
src/locales/es/login.json
src/locales/fr/login.json
src/locales/ja/login.json
src/locales/ko/login.json
src/locales/pt-BR/login.json
src/locales/ru/login.json
src/locales/zh-TW/login.json
src/locales/zh/login.json
Included review availability: This review used your included allowance. Your plan provides up to 8 included reviews per hour; 6 remain after this review.
- CodeQL js/incomplete-sanitization: the sources-dialog has-text selector
  escaped only quotes; a locale title containing a backslash could escape
  the escape character and break the selector string. Escape backslashes
  and quotes together.
- isDesktopBridgeOnlyDiff (CodeRabbit majors): the multiset line diff
  judged pure reorders as no-change, and any line merely mentioning
  desktopBridge/electronProxy counted as web-inert — a bridge ternary with
  changed web fallback values or swapped assignments would slip through as
  ui=false. The diff now separates additions from removals, treats a
  multiset-empty diff between different contents (a reorder) as
  non-inert, and only accepts lines shaped like bridge imports, bridge
  call statements, the isSupported() guard, or bare syntax; anything that
  assigns from the bridge or branches on it for web values stays
  non-inert.

Verified: the #603 head/base replay still yields ui=false (its diff is
purely additive bridge-shaped lines); #604 replay unchanged; node test
suite passes with new reorder/ternary regression cases.
Third CodeRabbit round on isDesktopBridgeOnlyDiff — the line-shape
whitelist still had three holes, all rooted in the same limitation: a
multiset diff plus per-line shapes cannot see what the unchanged lines
around a change mean. Replaced with a stronger formulation:

- webProjection: the in-order sequence of non-bridge lines must be
  byte-identical in both versions. This catches pure web reorders the
  multiset cannot see, including reorders mixed with additive bridge
  calls (the line-level reorder blind spot).
- guard-block analysis: every ADDED if (desktopBridge.isSupported())
  block (head) and every REMOVED one (base) must contain only
  bridge-shaped or bare-syntax lines. Wrapping or unwrapping an
  unchanged web statement makes its execution conditional on the desktop
  bridge — web-visible, previously invisible to line shapes.
- bridge call arguments are restricted to side-effect-free expressions
  (no nested calls, assignments or braces), so an argument cannot smuggle
  web-relevant side effects past the check.

Multiset equality between different contents (pure reorder) now falls
out of the projection comparison; byte-identical files stay inert;
anything unreadable or ambiguous stays non-inert (conservative: more
screenshots, never fewer). The #603 head/base replay still yields
ui=false; #604 unchanged; experiment baseline unchanged; new regression
tests cover guard wrap/unwrap, reorder+bridge mixes, and argument side
effects.
Fourth CodeRabbit round: moving an existing guard's closing brace to
absorb (or release) an unchanged web statement left the guard count and
the web line multiset untouched, so the diff passed as web-inert while
the statement's execution became conditional in the browser.

Replaced the occurrence-flag machinery with a single recursive web
projection: bridge-shaped and bare-syntax lines are omitted; a
desktopBridge.isSupported() guard block is transparent only when its own
projection is empty, otherwise it is emitted as a guard{...} token.
Web-inertness now means the base and head projections are identical,
which uniformly covers wrapping, unwrapping, boundary moves, web
reorders, and content edits; pre-existing guards that stay untouched
compare equal on both sides. Unbalanced braces degrade conservatively
(the remaining range is emitted raw).

#603/#604 replays unchanged; experiment baseline unchanged; new
regression tests cover both brace-move directions and the untouched
pre-existing guard.
Fifth CodeRabbit round: the guard-boundary scan counted braces per raw
character, so a } inside a comment or a string literal could close a
guard block on the scanner's behalf. Two versions whose guard wrapped
different statements could then compare equal and pass as web-inert.

Added braceDeltasPerLine: a single-pass scanner that skips line/block
comments and string/template literals (state carries across lines;
unterminated constructs at EOF return null and fail conservatively), and
projectRange now derives guard boundaries from those deltas. Comment-only
lines join the structural class (they cannot render). Known heuristic
edge: regex literals with unpaired braces/quotes may shift the scan and
degrade conservatively.

Verified: the CodeRabbit comment example and a string-brace variant are
non-inert; the #603 head/base replay still yields ui=false; #604 and the
experiment baseline are unchanged; the full test suite passes.
Sixth CodeRabbit round: a /}/ inside a regex literal (e.g.
void /[}]/.test(language)) was still counted as a code brace, so a guard
boundary could close on it and two differently-wrapped versions could
compare web-equal. The scanner now recognizes regex literals with the
standard previous-token heuristic (operator/opening bracket/keyword
before the slash, character-class tracking inside) and skips their
contents; misjudging a division as a regex is the direction that keeps
braces counted, so any residual imbalance degrades conservatively.

Both brace-move directions around a regex-bearing guard are covered by
new regression tests; #603/#604 replays and the experiment baseline are
unchanged.
Eighth CodeRabbit round: the operator whitelist included + - * % ~ ^, so
a slash after counter++ (division) was scanned as a regex start and its
closing slash swallowed the guard's closing brace, making two
differently-wrapped versions compare web-equal.

The whitelist now contains only token boundaries where a regex is the
only valid continuation (( [ { , ; = : ! & | ? > and the regex-allowing
keywords); every other slash is flagged ambiguous and the file stays
non-inert. There is no guessing path left: a slash either provably opens
a regex or the whole diff keeps its scene classification. Regression
tests cover both brace-move directions around counter++ / 2; the #603
replay, #604 and the experiment baseline are unchanged.
The incremental backward heuristics kept leaking: a line comment's body
could masquerade as a token in tokenBefore (whitespace skipping crossed
into comment text), and the newline handling left the scanner stuck in
the line-comment state after the first //, poisoning the whole file.
Both surfaced as the #603 replay regressing to ui=true.

Replaced the pair of scanners with one forward pass (analyzeCode) that
produces a per-character code mask (comments, strings, template literals
and regex contents are unmasked; the ambiguous-slash flag and an
unterminated construct at EOF mark the file unanalyzable), the per-line
brace deltas, and the mask. tokenBefore is now a mask-based backward
skip, so comment bodies can never masquerade as tokens regardless of
formatting. Verified: the CodeRabbit comment example, a string-brace
variant, and a template absorb all stay non-inert; additive bridge
diffs stay inert; the #603 head/base replay is ui=false again; #604 and
the experiment baseline are unchanged; the full suite passes.
This file contains hidden or bidirectional Unicode text that may be interpreted or compiled differently than what appears below. To review, open the file in an editor that reveals hidden Unicode characters.
Learn more about bidirectional Unicode characters
review: highghfind author score; see https://ghfind.com
1 participant
Add this suggestion to a batch that can be applied as a single commit.This suggestion is invalid because no changes were made to the code.Suggestions cannot be applied while the pull request is closed.Suggestions cannot be applied while viewing a subset of changes.Only one suggestion per line can be applied in a batch.Add this suggestion to a batch that can be applied as a single commit.Applying suggestions on deleted lines is not supported.You must change the existing code in this line in order to create a valid suggestion.Outdated suggestions cannot be applied.This suggestion has been applied or marked resolved.Suggestions cannot be applied from pending reviews.Suggestions cannot be applied on multi-line comments.Suggestions cannot be applied while the pull request is queued to merge.Suggestion cannot be applied right now. Please check back later.


 ghfind-review
Bot
added
the
review: high







Description
Resolves #594.
Background
When users use GitHub Fine-grained Personal Access Tokens (PATs) to manage stars:
DELETE /user/starred/{owner}/{repo}orPUT /user/starred/{owner}/{repo}on repositories belonging to other users or organizations often results in403 Forbidden(Resource not accessible by personal access token) or404 Not Foundif scoped via "Only select repositories" or blocked by organization PAT policies.userscope support.Changes
GitHubTokenPermissions.tsx, set the default active mode to'classic'and ordered the "Classic Token" tab first.public_repo,gist,user):https://github.com/settings/tokens/new?description=GithubStarsManager&scopes=public_repo,gist,userThis lets users generate a correctly scoped token with a single click.
zh,zh-TW,en,ja,ko,de,es,fr,pt-BR,ru).src/components/LoginScreen.test.tsxto verify default tab selection, limitation callouts, tab switching, and dynamic creation URLs.Verification
npm run check:i18n(passed)npm run typecheck(passed)npm run lint(passed)npm test -- --run(all 195 test files, 2416 tests passed)Summary by CodeRabbit