feat: implement MDBList OAuth 2.0 Device Code flow - #738
Himanth-reddy wants to merge 7 commits into
Conversation


 github-actions
Bot
added
the
area: android

- Implement standard OAuth 2.0 Device Authorization Grant for MDBList
- Add device code request and polling token endpoints in MdbListApi
- Store per-profile OAuth bearer token, refresh token, and expiration in SyncProviderStore
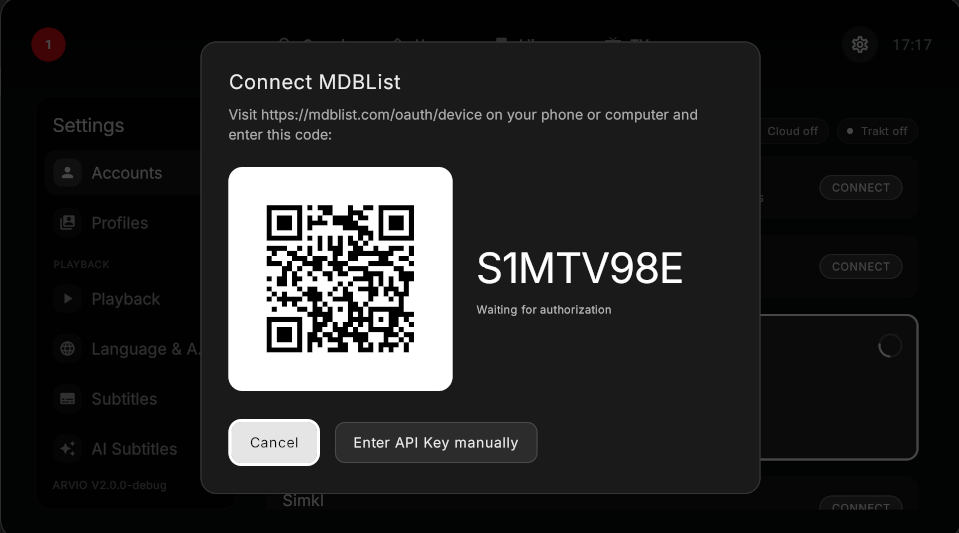
- Integrate device authorization modal with QR code on TV and mobile
- Sanitize activation instruction URL to display cleanly up to /device without query params
- Clean up background account rows to avoid inline auth text and background spinners during authentication
- Remove manual API key input dialogs and legacy validation logic

2052768 to
71c50c4
Compare

|
Thanks for working on this, Himanth. QR-code login would make MDBList much easier to connect on TV. The rebase has resolved the earlier merge conflicts, but let's keep this open until the authentication lifecycle is complete. These are the remaining issues I found:
Please add tests for expiry/renewal, legacy-key disconnect, cloud round-trips and disconnects, polling errors, and profile switches. Then verify actual device-code login and cross-device/web behavior with the registered client ID. A successful initial login alone doesn't cover these cases. I stopped my local fix attempt and discarded those edits. Nothing has been pushed or merged from that attempt; your PR and commits remain unchanged. |
…ist OAuth lifecycle

- Serialize token renewal via Mutex in MdbListRepository, preserving refresh tokens on omission and handling renewal errors gracefully
- Separate OAuth (Authorization: Bearer <token>) from legacy API key (?apikey=<key>) across Android, web proxy, and web tracking client
- Ensure complete disconnect clears both OAuth and API key credentials across local storage and cloud sync
- Restore manual API key connect dialog and fallback when MDBList client ID is absent
- Fix device polling error parsing using single read of errorBody and RFC 8628 code handling
- Enforce profile scoping during polling and token renewal to prevent cross-profile pollution
- Restore Trakt and Simkl isWorking indicators and cancellation callbacks in SettingsScreen
- Add MdbListAuthLifecycleTest unit test suite covering renewal serialization, omission preservation, disconnect, error parsing, and auth separation
- Add Netlify cloud sync push test for MDBList OAuth credentials
 github-actions
Bot
added
documentation
|
Thanks, Himanth. I pushed the remaining code fixes to this PR, preserving your original commits and authorship. Fixed the merge with current main; guarded Android refresh against disconnect/new-login races; kept provider changes bound to the correct profile; added web renewal and OAuth support for watched history/watchlist writes; preserved API-key fallback; fixed the TV fallback button handling; and wired the existing MDBLIST_CLIENT_ID repository secret into signed Android and web builds. Failed authentication is no longer treated as a successfully empty Android watchlist. Local verification passed: 26 Android authentication/store tests, 743 web tests, 113 backend tests, TypeScript checks, and diff checks. GitHub CI is running on the updated head. One external check still needs confirming before I merge: actual device-code authorization and refresh using ARVIO's registered public MDBList client, without embedding a client secret. The repository secret exists, but that alone does not establish that the client is registered for these grants. Could you confirm the public client ID/registration and test a real TV login, renewal, and web/cloud restore? Please do not post a client secret or user tokens. I added docs/MDBLIST_OAUTH.md with the configuration and live-check checklist. Leaving this open until that is verified; the automated tests use synthetic credentials and cannot establish live MDBList authorization. |
# Conflicts:
#	app/src/main/kotlin/com/arflix/tv/ui/screens/settings/SettingsViewModel.kt

|
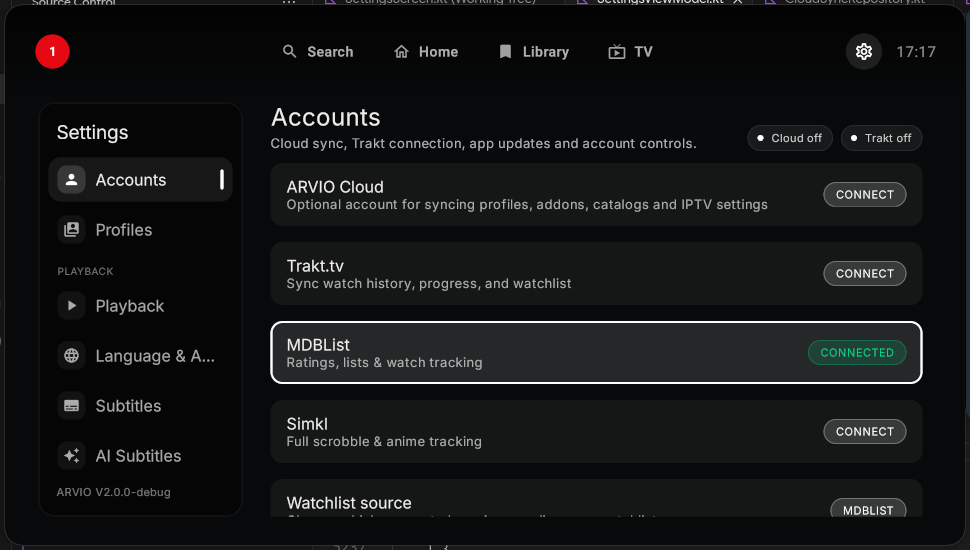
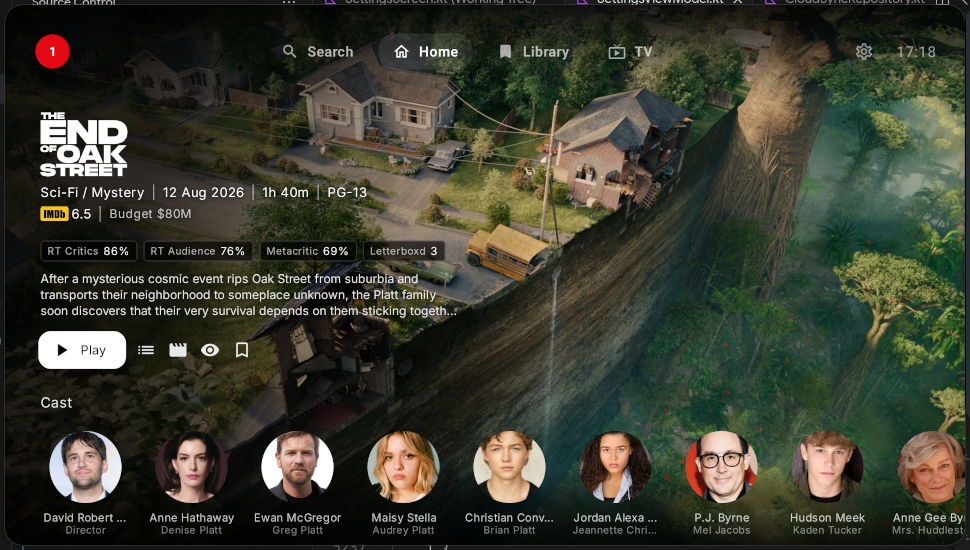
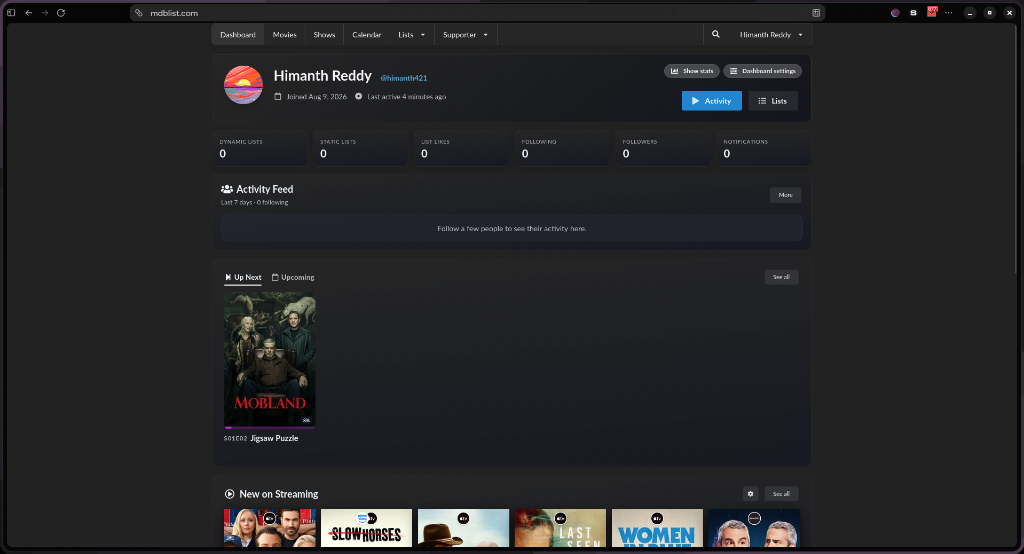
I have tested and verified live MDBList OAuth 2.0 device authorization, real TV login, and watch history synchronization on Android TV (
Live Verification Screenshots
|
2 participants


Summary
Implements the standard OAuth 2.0 Device Code flow (RFC 8628) for MDBList across Android TV and mobile platforms, bringing it into parity with the Trakt and Simkl device linking experiences while removing legacy manual API key entry.
Changes
MdbListApi.kt):oauth/device-authorization/endpoint for requesting device code, user code, and verification URI.oauth/token/endpoint for polling token exchange.MdbDeviceAuthorizationResponse,MdbDeviceTokenRequest,MdbTokenResponse).@Header("Authorization")support to all MDBList API endpoints.SyncProviderStore.kt):mdblist_access_token,mdblist_refresh_token, andmdblist_token_expires_at.MdbListRepository.kt,SettingsViewModel.kt):authorization_pending,slow_down,expired_token,access_denied).SettingsScreen.kt):TraktActivationModaldialog with QR code and external browser launch./device(https://mdblist.com/oauth/device), omitting query parameters while keeping full URL for QR code and browser buttons.AccountRow/TrackingServiceRowto avoid inline text expansion and spinners while the modal dialog is open in the foreground.Constants.kt,secrets.defaults.properties):MDBLIST_CLIENT_IDconfiguration key.Verification
./gradlew :app:assembleSideloadDebug -PincludeX86Abis=true— Successful.emulator-5556) and Android Phone (emulator-5554).graphify update ..